Enterprise ISMS & GRC Management Platform
A comprehensive enterprise ISMS and GRC platform designed to manage information security processes, risks, controls, audits, assets, incidents, documentation, and compliance workflows through a centralized system.
Project Overview
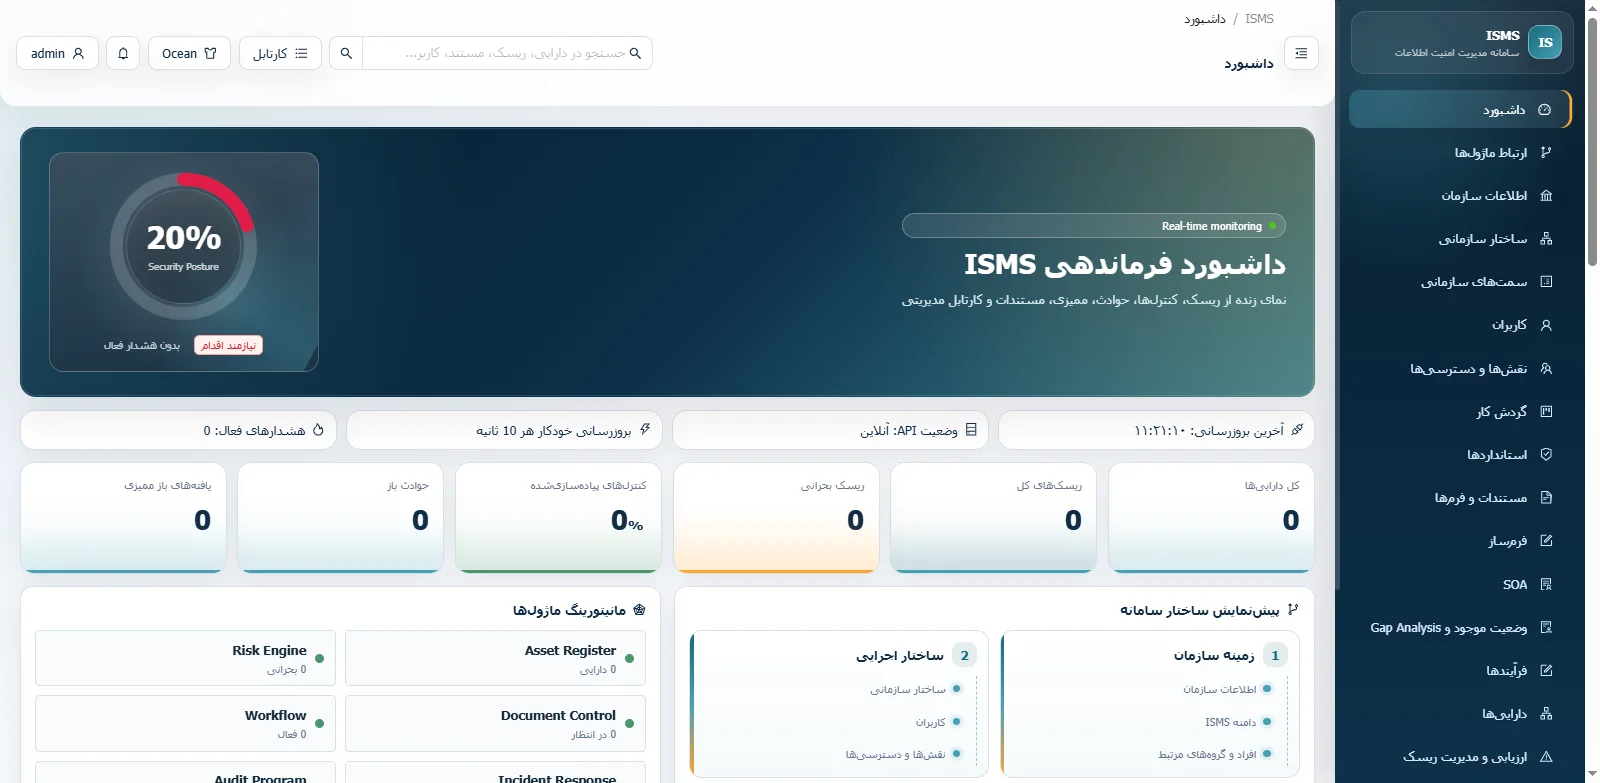
This project is a comprehensive enterprise ISMS and GRC management platform designed to centralize and automate information security governance, risk management, compliance, and operational security processes. The system provides organizations with an integrated environment for managing information assets, security risks, controls, audits, incidents, documentation, organizational structures, objectives, standards, workflows, and compliance activities. The platform was developed using a modern full-stack architecture with React and TypeScript on the frontend and NestJS, TypeORM, and MariaDB on the backend. The backend follows a modular architecture and provides REST APIs for the different ISMS domains. Authentication and authorization are implemented using JWT, role-based permissions, access guards, input validation, rate limiting, CORS restrictions, and security headers. The system also includes a browser-based setup wizard for initial installation and database configuration, allowing the application to initialize the required database structure, migrations, organization information, and administrator account. Key modules include: • Information Security Risk Management • Statement of Applicability (SoA) • Gap Analysis • Asset Management • Incident Management • Audit Management • Document Management • Standards and Controls Management • Organizational Structure Management • Processes and Objectives • Workflow Management • Reports and Dashboards • Roles and Permissions • User Management • Audit Logs • Notifications • Knowledge Base • Dynamic Form Management The platform is designed as a scalable foundation for organizations that need a centralized solution for managing ISMS and GRC activities.
Technical Challenge
One of the main technical challenges was designing a large modular architecture capable of supporting multiple ISMS and GRC domains while keeping the system maintainable and scalable. The platform required a consistent data model for risks, assets, controls, audits, incidents, documents, organizational entities, permissions, and workflows. Another major challenge was implementing secure authentication and authorization across a large number of modules while maintaining fine-grained access control. The project also required database migrations, installation automation, input validation, API standardization, audit logging, rate limiting, and secure production configuration.
Solution
I designed the system using a modular full-stack architecture. The frontend was implemented with React, TypeScript, Vite, Ant Design, React Query, React Hook Form, and Zod. The backend was developed with NestJS, TypeORM, and MariaDB using separate modules for each ISMS domain. JWT-based authentication, role and permission management, guards, request validation, secure headers, CORS restrictions, rate limiting, and centralized exception handling were implemented to secure the application. Database migrations and seed mechanisms were developed to maintain the application schema, and a browser-based setup wizard was created to simplify installation and initial configuration. This architecture allows new ISMS modules and organizational workflows to be added without tightly coupling them to the rest of the system.